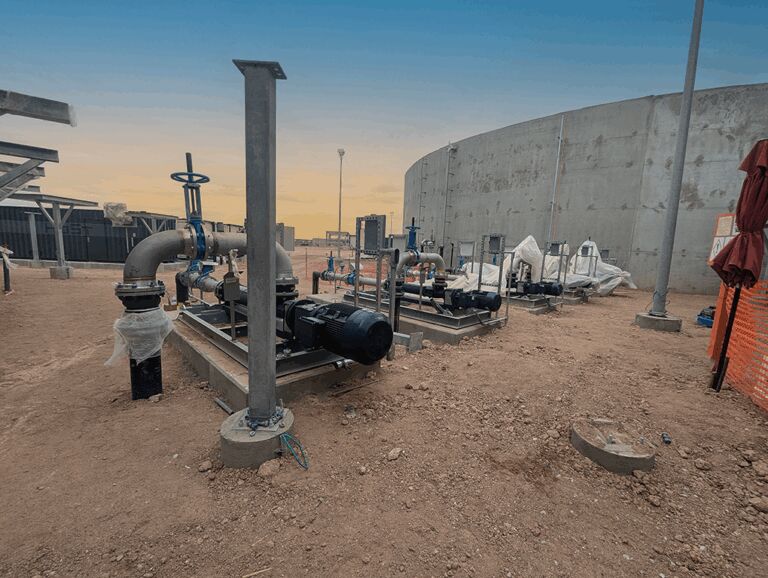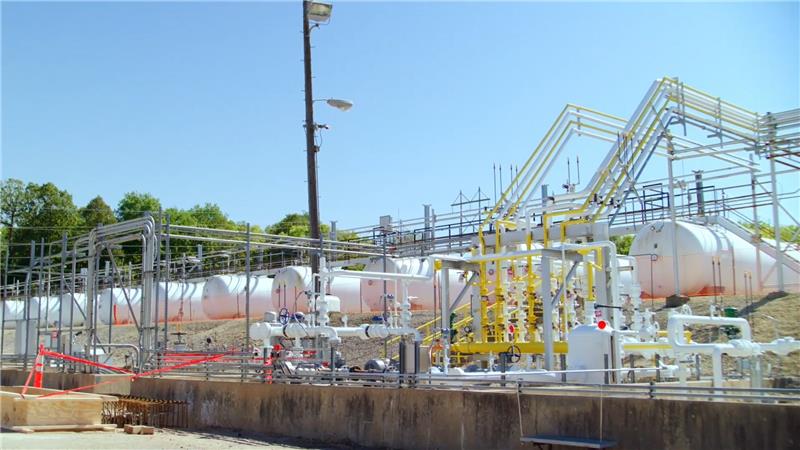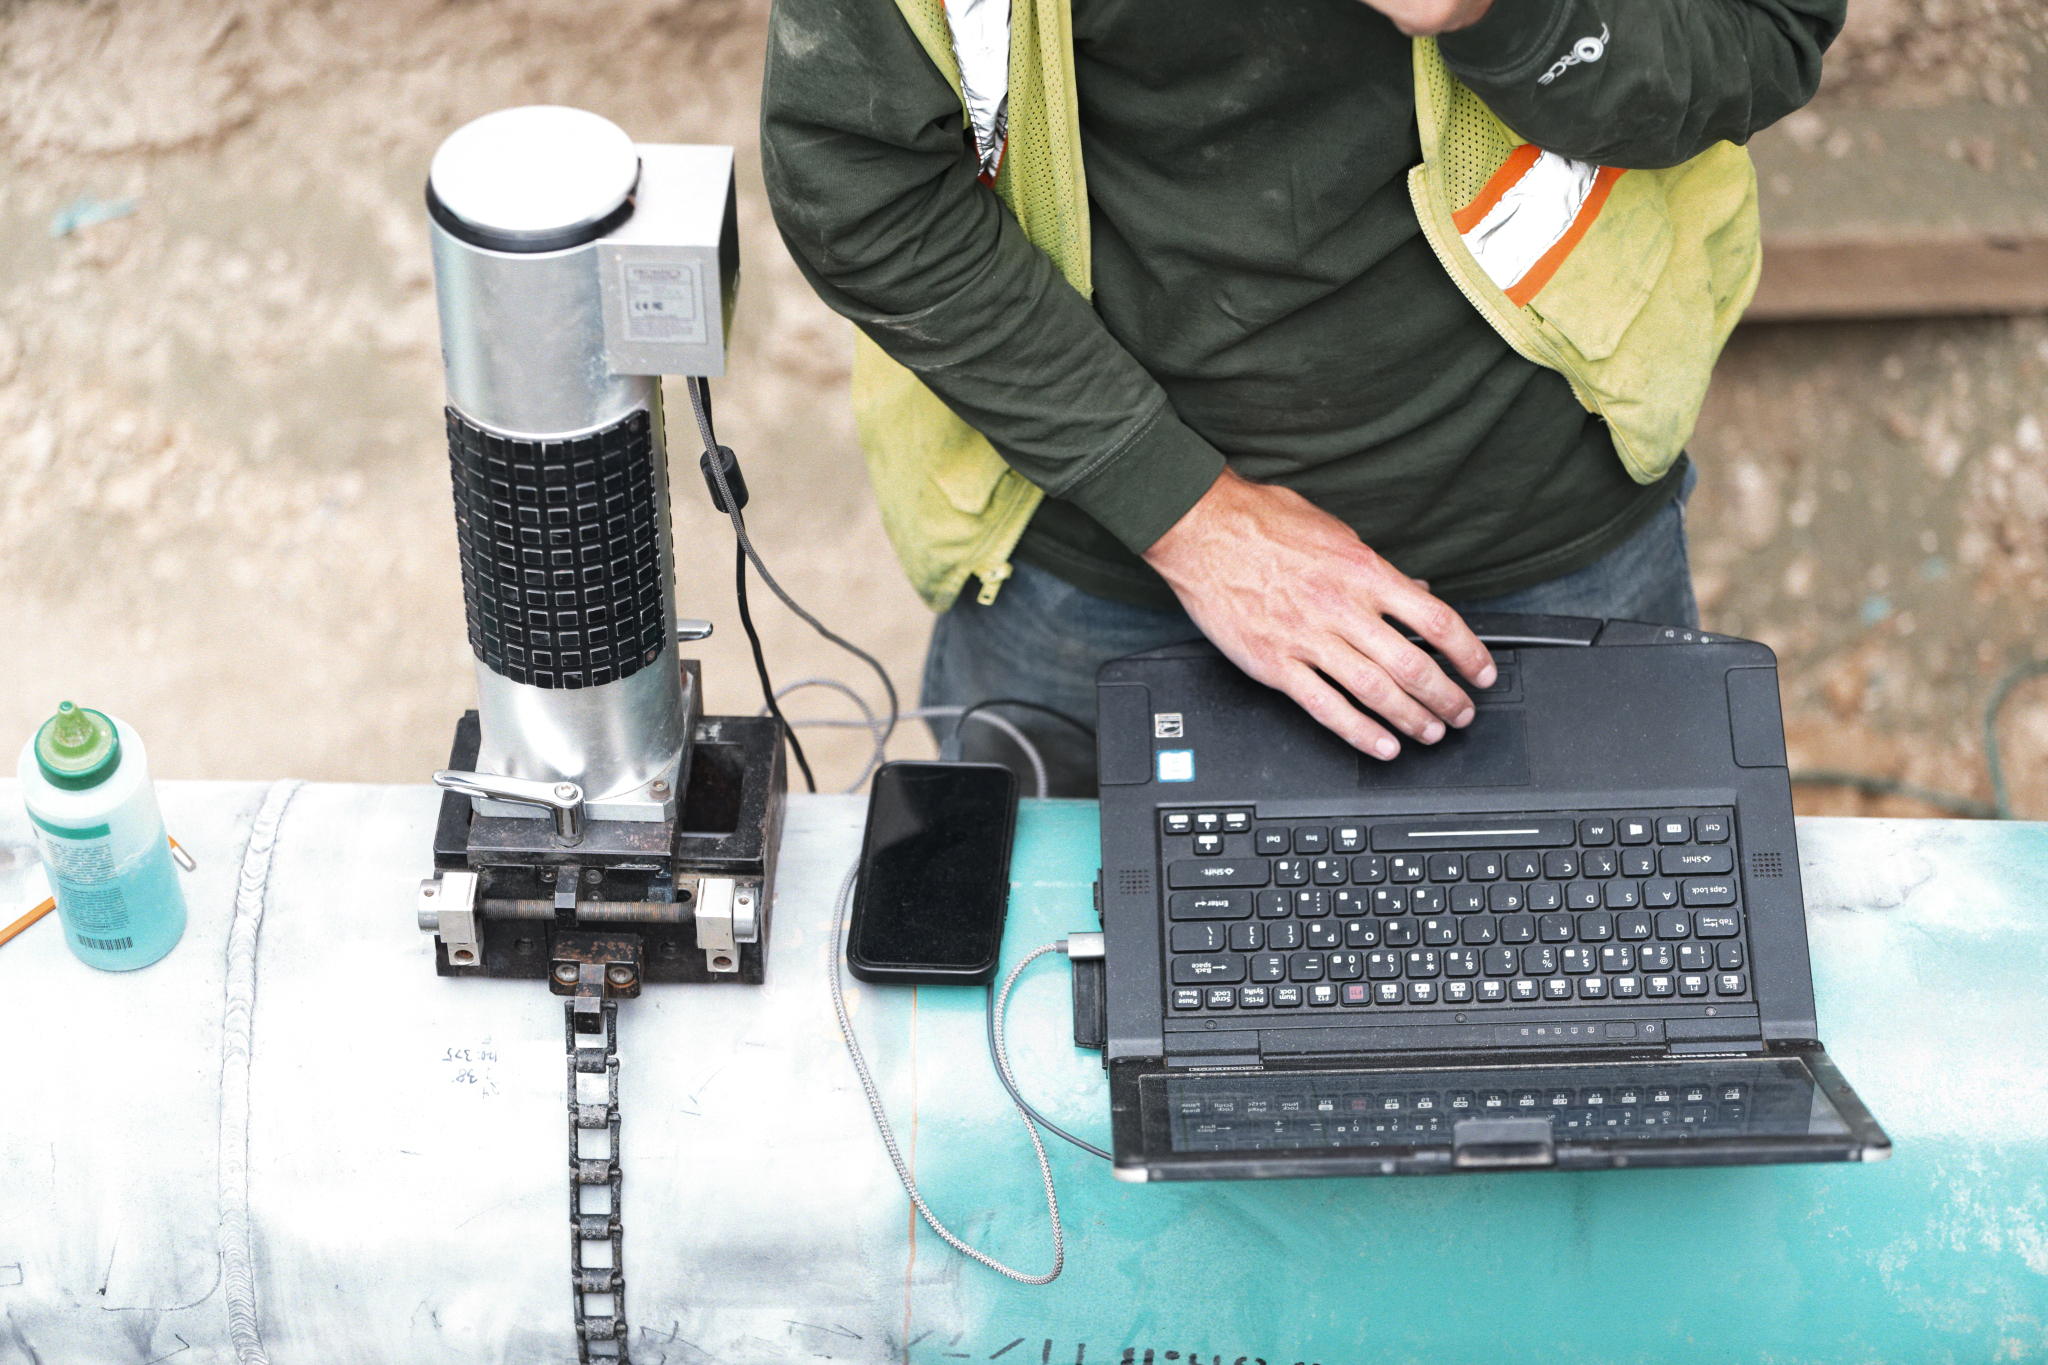
Our ISA/IEC 62443 certified in-house experts take proven strategic steps to understand our client’s network before auditing/assessing their system, modeling the system architecture, and developing a Risk Assessment Report before proposing an Implementation Plan, and Incident Response Plan to mitigate these vulnerabilities.
The action plan includes deliverables to meet or exceed current industry regulations and ensure compliance. Our extensive experience with designing, engineering, and constructing industrial facilities allows us to bridge the gap between client systems and cybersecurity regulations.
Contact us at OTCyberSecurity@camposepc.com